Leaked backend data from "no-KYC" swap Wagyu.xyz links 38k+ crypto orders, Monero destinations, and user IPs
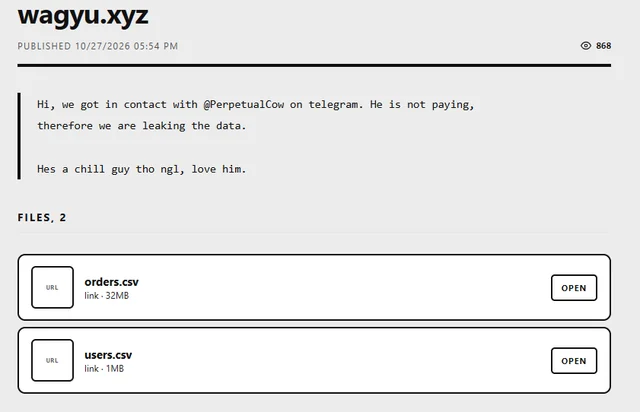
Monero's cryptography wasn't broken at all, but the leak shows how off-chain centralized databases create a huge privacy hole. Key Takeaways: Monero is fine, centralized swap retention isn't: Monero's on-chain math still holds up. However, Wagyu stored incoming deposit hashes (BTC/ETH/SOL), outgoing XMR receiving addresses, timestamps, and client IPs together in the same database rows. Direct correlation risk: The leak contains 4,580 completed cross-chain-to-XMR orders that map the original public deposit TX directly to the native XMR receiving address and the user's IP. It also goes the other way for XMR exits (accepting XMR and logging the transparent ETH/BTC destination and IP). "Deleted" orders weren't actually deleted: Over 4,000 orders have a userDeletedAt timestamp, meaning users thought they cleared their history from the UI, but the full trade metadata and IPs remained sitting in the backend. What it means for users: The data doesn't magically trace funds once they move inside Monero, nor does an IP alone equal a real-world identity (VPNs, Tor, NAT
이 기사 공유하기
교환하러 가기
교환 시작공개 RSS 피드를 전재한 것으로 정보 제공 목적이며 투자 자문이 아닙니다. VeilSwap과 제휴하지 않습니다.